Intelligence Driven Defense [Lockheed Martin]
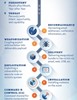
See how the Lockheed Martin Computer Incident Response Team (LM-CIRT) used analysis obtained through the intrusion kill chains and robust indicator maturity to successfully detect and mitigate an intrusion leveraging a "zero-day" vulnerability.
This whitepaper also reviews:
- Using a kill chain model to describe phases of intrusions
- Mapping adversary kill chain indicators to defender courses of action
- Identifying patterns that link individual intrusions into broader campaigns
- Understanding the iterative nature of intelligence gathering form the basis of intelligence-driven computer network defense (CND)
Please note: That all fields marked with an asterisk (*) are required.