Infographics
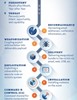
Intelligence Driven Defense [Lockheed Martin]
See how the Lockheed Martin Computer Incident Response Team (LM-CIRT) used analysis obtained through the intrusion kill chains and robust indicator maturity to successfully detect and mitigate an intrusion leveraging a "zero-day" vulnerability.
This whitepaper also reviews:
- Using a kill chain model to describe phases of intrusions
- Mapping adversary kill chain indicators to defender courses of action
- Identifying patterns that link individual intrusions into broader campaigns
- Understanding the iterative nature of intelligence gathering form the basis of intelligence-driven computer network defense (CND)
ICS DACH Plot Thickens for Cyber Security
In 2015, the upper house of the German parliament, the Bundesrat, approved the IT-Sicherheitsgesetz or IT Security Law.
This act mandated that more than 2,000 “Operators of Critical Infrastructure” should implement a raft of new information security standards and comply with notification obligations within a two year period or face severe penalties. Approaching the half way mark of 2017, that 24 month stay of execution is almost up. Is industry ready?
Since the passage of the IT-Sicherheitsgesetz, companies that employ industrial control systems (ICS) as an integral part of their day-to-day functionality have had a long time to assess their capabilities and weaknesses.
In the run up to our ICS Cyber Security DACH event in Germany, we spoke with leading ICS Security professionals from across the DACH region to learn just where they are in their cyber security journey. Some of the answers are rather disconcerting….